Environment Files & Secret Redaction
Load variables from .env files in curl-runner, with environment-specific overrides, a clear precedence order and automatic secret redaction in output.
Feature overview →Load variables from .env files with automatic secret protection in CLI output.
Overview
curl-runner automatically loads variables from .env files and redacts sensitive values in output. This keeps secrets safe when sharing logs or terminal output.
- .env Support: Auto-load variables from
.envfiles - Secret Redaction: Automatically mask sensitive values
- Pattern Detection: Auto-detect common API key formats
Basic Usage
Create a .env file in your project root. Variables are automatically loaded and available via ${VAR_NAME} syntax.
# .env
API_URL=https://api.example.com
API_VERSION=v1

# Secrets (automatically redacted in output)
SECRET_API_KEY=sk_live_abc123def456
SECRET_TOKEN=ghp_xxxxxxxxxxxx# api.yaml
request:
url: ${API_URL}/users
method: GET
headers:
Authorization: Bearer ${SECRET_API_KEY}
X-Api-Version: ${API_VERSION}Environment Overrides
Use environment-specific files to override values for different deployments.
# .env (base defaults)
API_URL=https://api.example.com
DEBUG=false

# .env.local (local overrides, gitignored)
DEBUG=true

# .env.staging (environment-specific)
API_URL=https://staging.api.example.com

# .env.staging.local (local staging overrides)
API_URL=https://my-staging.api.example.com
Priority Chain
Files are loaded in order, with later files overriding earlier values.
# Priority (lowest to highest):
# 1. .env              - Base defaults
# 2. .env.local        - Local overrides (gitignored)
# 3. .env.{env}        - Environment-specific
# 4. .env.{env}.local  - Local environment overrides

# Example: with --env staging
# Loads: .env -> .env.local -> .env.staging -> .env.staging.local
CLI Options
Use the --env flag to select an environment.
-
-e,--env <name>: Select environment (loads.env.{name}files) -
--no-redact: Disable secret redaction in output (not recommended)
# Use staging environment
curl-runner api.yaml --env staging
curl-runner api.yaml -e staging

# Use production environment
curl-runner api.yaml --env production

# Disable secret redaction (not recommended)
curl-runner api.yaml --no-redact
Configuration
Set defaults in curl-runner.yaml.
# curl-runner.yaml
global:
  env:
    environment: staging    # Default environment
    redactSecrets: true     # Enable redaction (default)
  variables:
    # These override .env values
    CUSTOM_VAR: "from-config"
Secret Redaction
Secrets are automatically redacted in URLs and curl command output.
SECRET_ Prefix
Variables starting with SECRET_ are always redacted.
# Variables starting with SECRET_ are automatically redacted
SECRET_API_KEY=sk_live_abc123
SECRET_DATABASE_URL=postgres://user:pass@host/db
SECRET_JWT_TOKEN=eyJhbGciOiJIUzI1NiIs...

# Regular variables are NOT redacted
API_KEY=public_key_123
DATABASE_HOST=localhost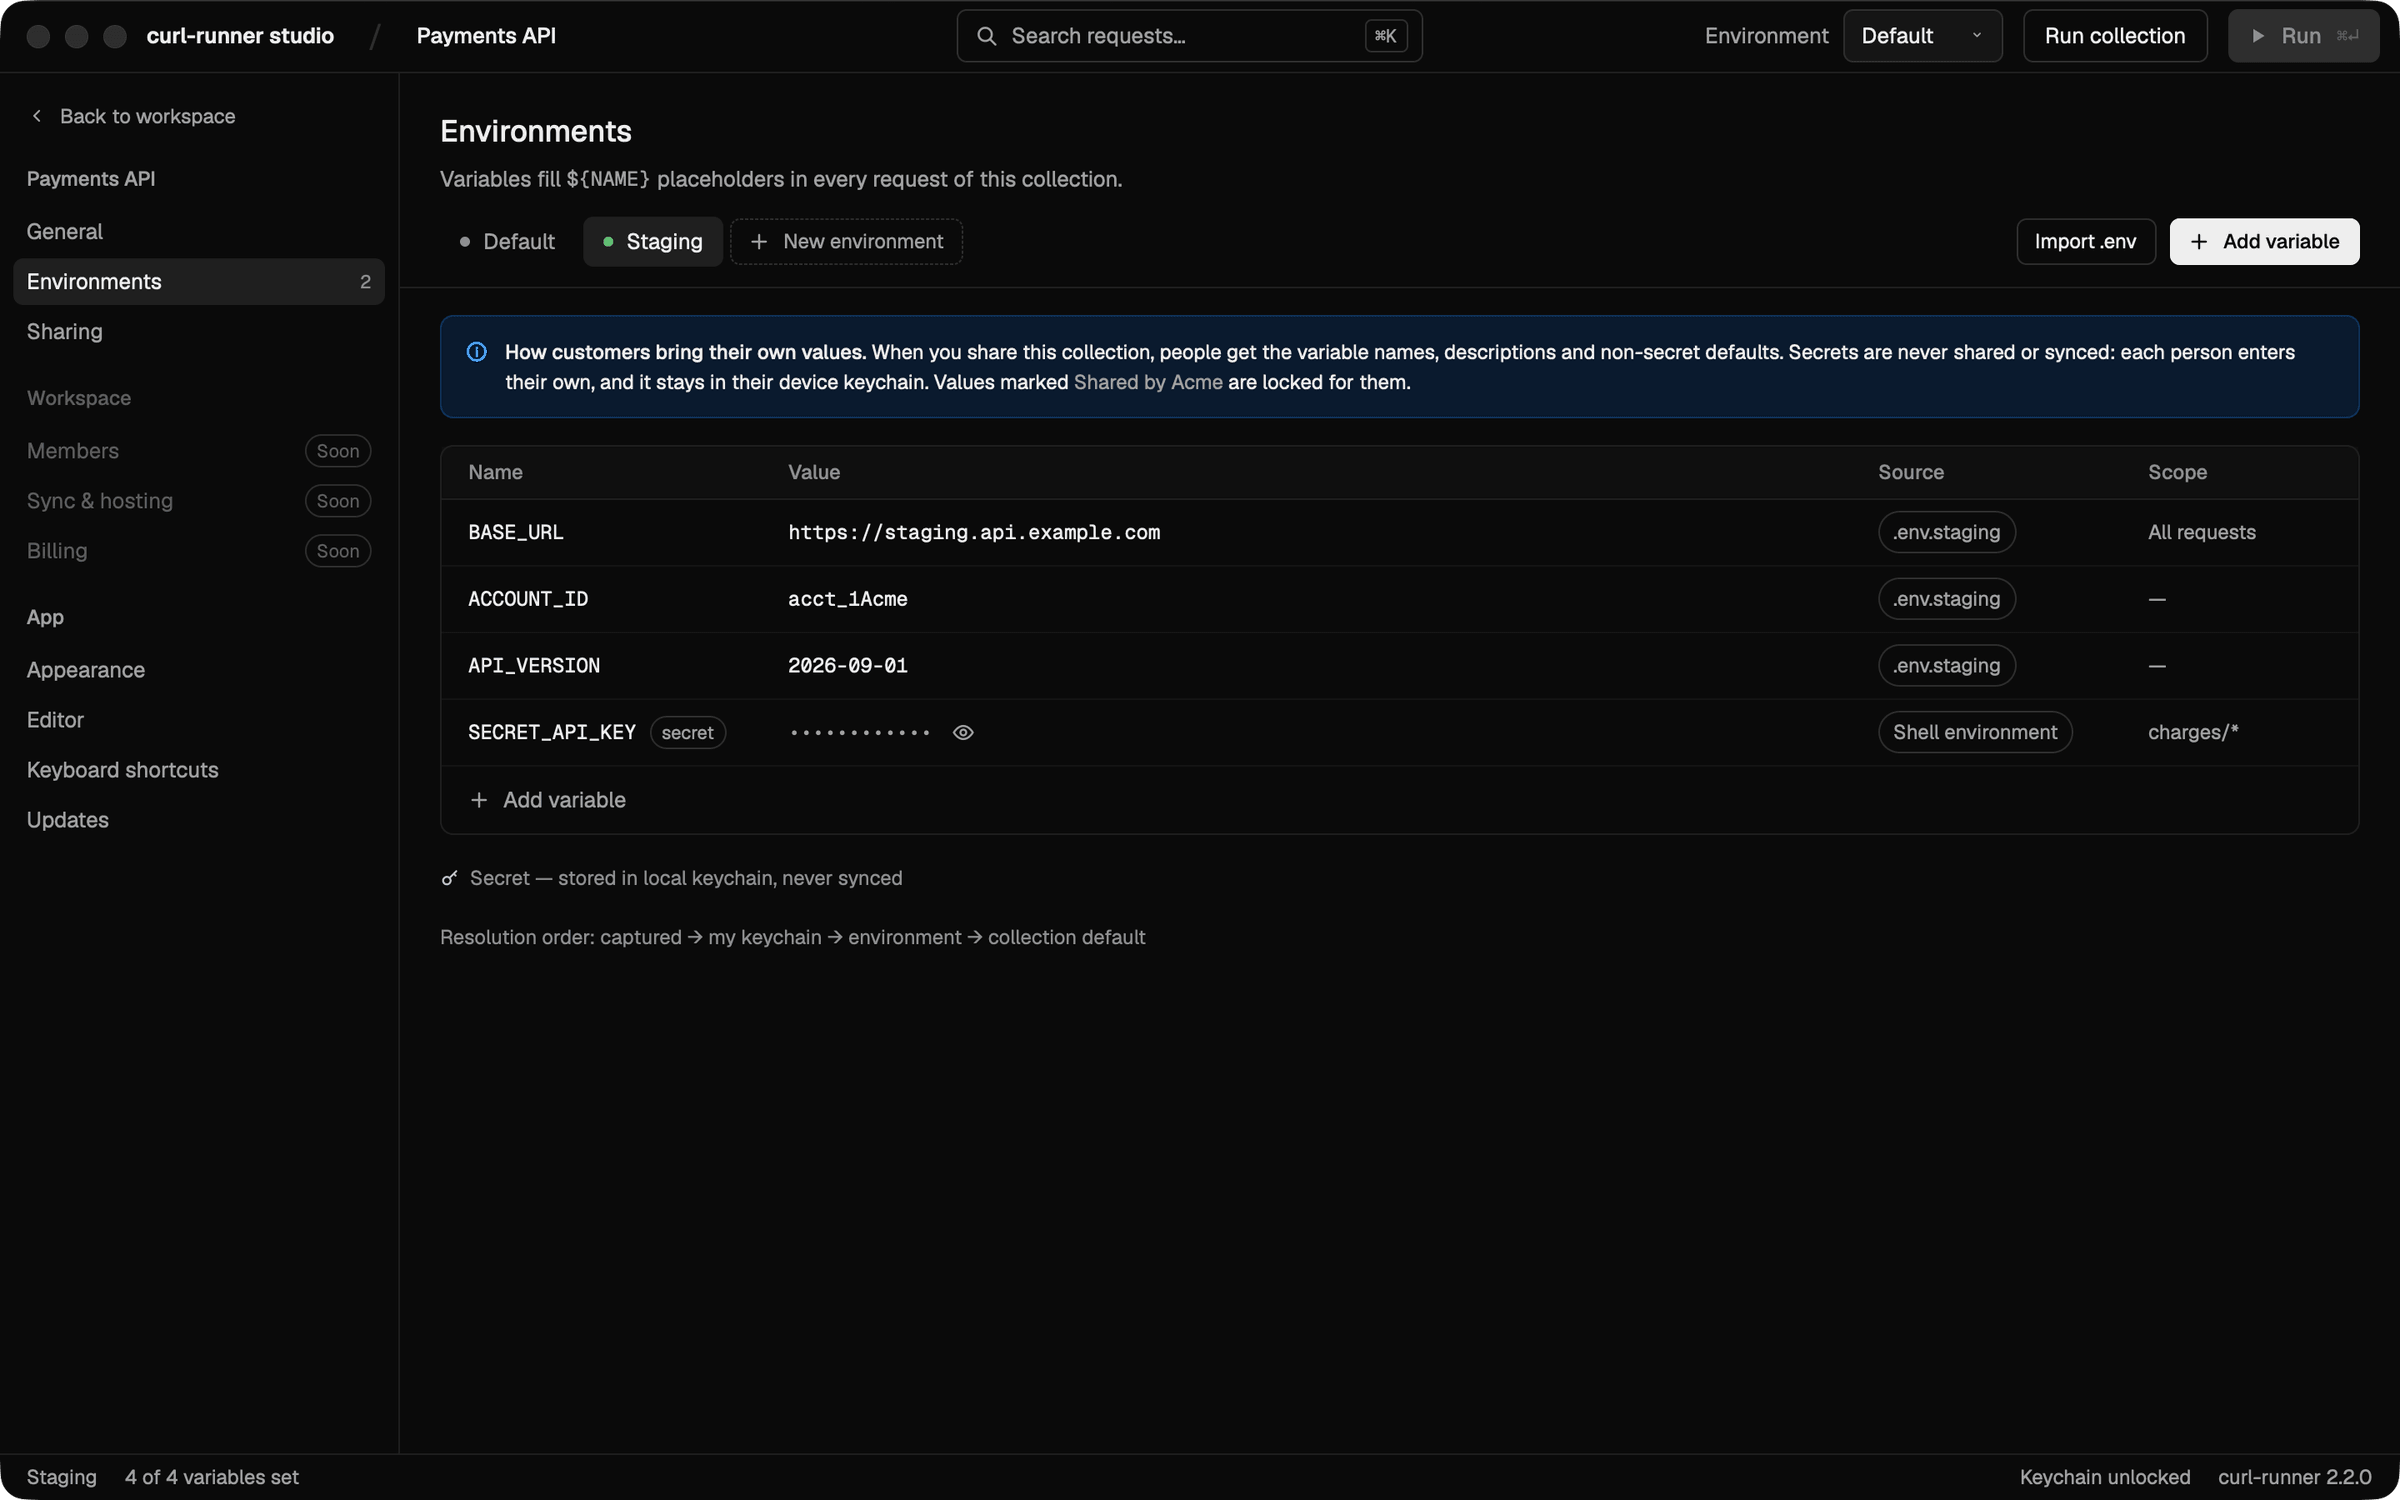
.env.staging, and the SECRET_ variable's value stays masked. Shown in curl-runner studio, a macOS preview.Pattern Detection
Common API key patterns are automatically detected and redacted, even without the SECRET_ prefix.
# These patterns are automatically detected and redacted:

# Stripe keys
sk_live_... / sk_test_... / pk_live_... / rk_live_...

# AWS credentials
AKIA... (AWS Access Key IDs)

# GitHub tokens
ghp_... / gho_... / ghu_... / ghs_... / ghr_...

# NPM tokens
npm_...

# Slack tokens
xoxb-... / xoxp-...

# Paddle keys
pdl_...

# OpenAI keys
sk-...

# Anthropic keys
sk-ant-api03-...

# Bearer tokens
Bearer <40+ char token>
Redaction in Output
Secrets appear as [REDACTED] in output.
# api.yaml sends:  X-Api-Key: ${SECRET_API_KEY}

# Without redaction (--no-redact)
$ curl-runner api.yaml --dry-run --no-redact
  curl -H 'X-Api-Key: sk_live_abc123def456' ...

# With redaction (default)
$ curl-runner api.yaml --dry-run
  curl -H 'X-Api-Key: [REDACTED]' ...
Git Ignore
Always gitignore local and production env files to prevent accidental commits.
# .gitignore
.env.local
.env.*.local
.env.production
Best Practices
- Recommended
- Prefix secrets with
SECRET_ - Use
.env.localfor personal overrides - Keep
.envin git with safe defaults - Gitignore all
.localand production files - Use environment-specific files for staging/production
- Prefix secrets with
- Avoid
- Using
--no-redactin shared terminals - Committing
.env.localor.env.production - Storing production secrets in base
.env - Sharing terminal output without reviewing for secrets
- Using
Curl ⇄ YAML Conversion
Convert curl commands to curl-runner YAML and back. Paste a curl command, get clean YAML. Convert YAML specs to canonical curl commands.
Studio (preview)
curl-runner studio is a macOS app for your YAML request files: live validation, runs, checks, retries, environments and history. A preview, built from source.